KDDI Launches AI Vulnerability Management Service
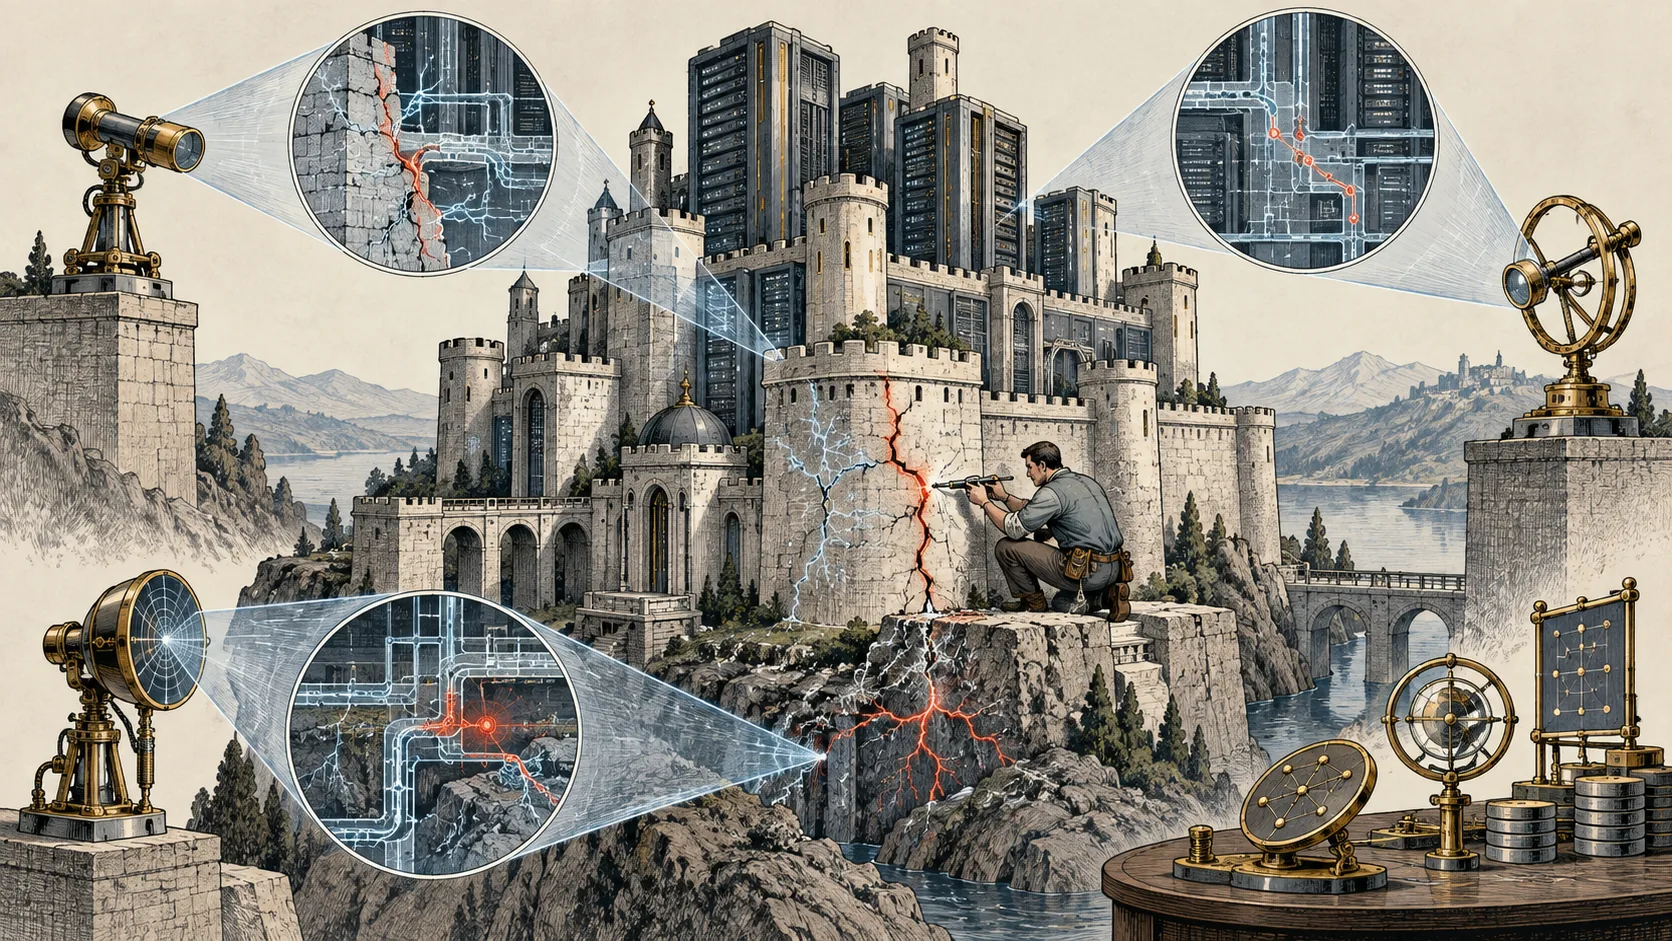
- •KDDI begins a service that assesses IT asset vulnerabilities and handles remediation, including configuration changes and system fixes
- •Rack and KDDI combine three types of assessments to expose attack paths and configuration weaknesses
- •Multiple AI agents analyze code and prioritize vulnerabilities that pose higher exploitation risks
KDDI began offering its AI Vulnerability Management Solution on October 28, 2026, to assess vulnerabilities in IT assets and manage remediation. It identifies risks across networks and systems, ranks issues by likelihood of exploitation and business impact, and provides end-to-end support through the KDDI Group, including configuration changes and system fixes.
The service follows CTEM, a framework for continuously managing an organization’s exposure to threats. It manages discovery of the attack surface, vulnerability assessment, prioritization of countermeasures, and ongoing improvement. KDDI says many companies struggle to track all IT assets, decide which issues to address first, and maintain oversight across overseas offices and affiliates, driving demand for CTEM.
The service combines three assessments: Rack’s attack-path assessment, plus KDDI’s AI network configuration assessment and AI software assessment. Together, they reveal attack routes that may be hard to find through a single assessment and identify issues to address first.
The attack-path assessment examines internet-facing systems across IT environments, including overseas offices and subsidiaries, from an attacker’s perspective. It checks IT assets accessible from outside and exposed ports to show where an attack could enter.
In the AI network configuration assessment, AI informed by KDDI’s expertise analyzes network settings, including firewalls, and automatically identifies weaknesses such as overly broad traffic permissions and missing multi-factor authentication (MFA). It also checks vulnerabilities in network equipment and operating systems. Engineers review the AI’s findings before KDDI provides a diagnostic report and proposed improvements.
For the AI software assessment, multiple AI agents using frontier AI analyze source code to detect coding flaws and potential vulnerabilities. They use guidance including the U.S. Cybersecurity and Infrastructure Security Agency’s vulnerability response directive BOD 26-04 to prioritize vulnerabilities with higher exploitation risks. The process automates triage, or ranking issues by response priority, which previously required time-consuming manual work.
The service covers corporate groups operating in Japan and overseas, as well as their business partners. KDDI says it will provide the same level of security management to headquarters, overseas offices, subsidiaries, and partner companies. The announcement gave no performance figures or pricing beyond the start date. KDDI says it handles the process from risk assessment through configuration changes and system fixes.