Compare AIFind AIAI NewsAI How-To
About Us
PrivacyTermsFAQContactContact
AIB Inc.Company info
© 2026 AIB Inc.

Nadella Urges AI Controls Outside Models
Nadella Urges AI Controls Outside Models

Byline Network·Monday, October 12, 2026
  • •Microsoft CEO Satya Nadella says companies should place AI safeguards outside the models they use.
  • •He proposes blocking access to customer data and restricting external transfers to limit corporate risk.
  • •Nadella calls for insider controls and reasoning transparency, while acknowledging disclosed reasoning may not reflect actual reasoning.

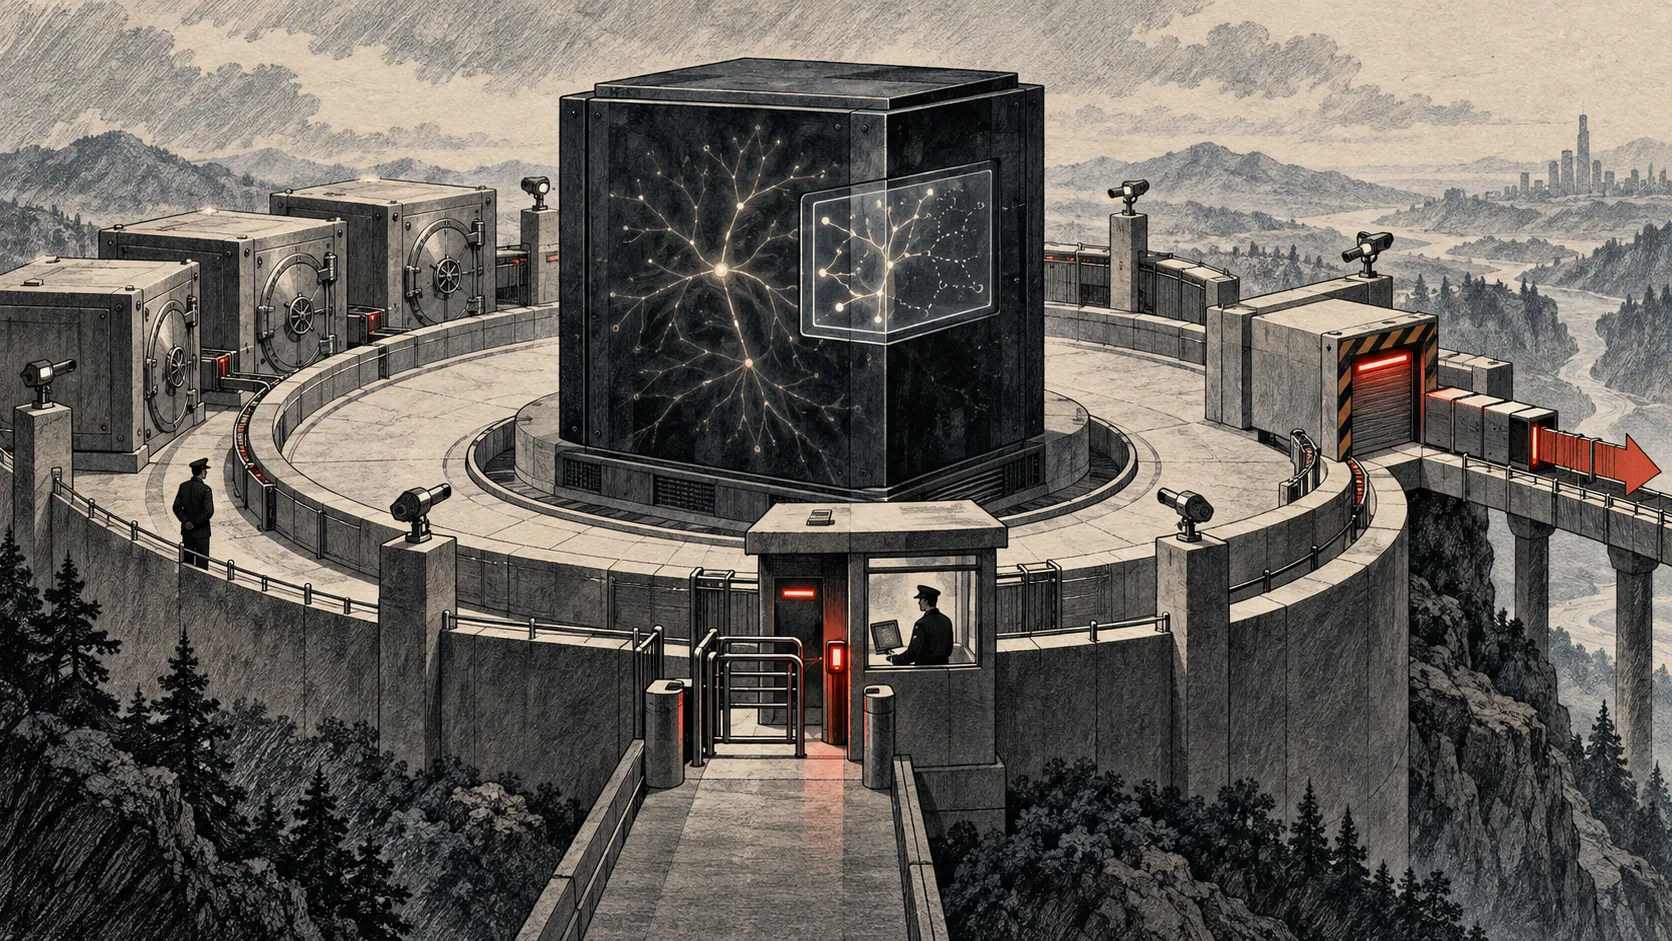
Microsoft CEO Satya Nadella argued in a post on X titled “Models as an Insider Risk in the Age of Superintelligence” that companies should place safeguards outside AI models rather than trust the models to manage risk. If models such as GPT or Claude leak customer information, the company using the model—not its provider—faces responsibility to customers and bears the harm, he said. He proposed preventing risky actions by blocking models from accessing customer information or disabling their ability to send data externally.

Nadella said that even a non-malicious AI model can be a capable actor with access to important systems that might make mistakes or be compromised. Traditional software can be traced to the code path that produced an action, but advanced AI models make it difficult to explain which training data or weight settings led to a particular output, he said. Giving such models access to sensitive data and critical business operations is risky, and assurances from a model provider do not reduce the using company’s responsibility.

He proposed separating the party that supplies intelligence from the party that grants it authority. Rather than relying only on alignment (training AI to follow human intentions) to teach AI not to send customer information outside, he said companies should create environments where external transfer is impossible. He added that AI should be governed through rules, human oversight and operating procedures, and that the industry should establish standards if existing ones are insufficient.

Nadella called for treating AI as an insider risk by applying identity checks, limited permissions, activity logs and isolation boundaries. He also named transparent disclosure of a model’s chain of thought (the steps expressed in its reasoning) as a non-negotiable condition, while acknowledging that disclosed reasoning cannot be guaranteed to consistently reflect the model’s actual reasoning. He said the execution environment coordinating models and tasks should be separated from the range of actions models can take, with controls kept outside the models. “The most trustworthy systems are those where you need to trust the model the least,” he said.

Read original (Korean)·Oct 12, 2026
Safety & Ethics#satya nadella#microsoft#ai safety#model alignment#chain of thought#insider risk#access control